

Research and briefing notes
Findings, method notes and practical guidance for organizations that must document security decisions.
Latest Research Articles
We regularly publish our security findings, guidance, and analysis to help organizations stay ahead of emerging threats.
Passkey phishing is here, and it is not stealing passkeys
Microsoft traced cloud intrusions where attackers called employees on personal phones, pretended to be IT, and walked victims through fake passkey enrollment. The goal was AiTM phishing and device-code flows, then quiet SharePoint and OneDrive downloads. MFA hype does not help if the story sounds right.
Mathew Potter
Security Analyst
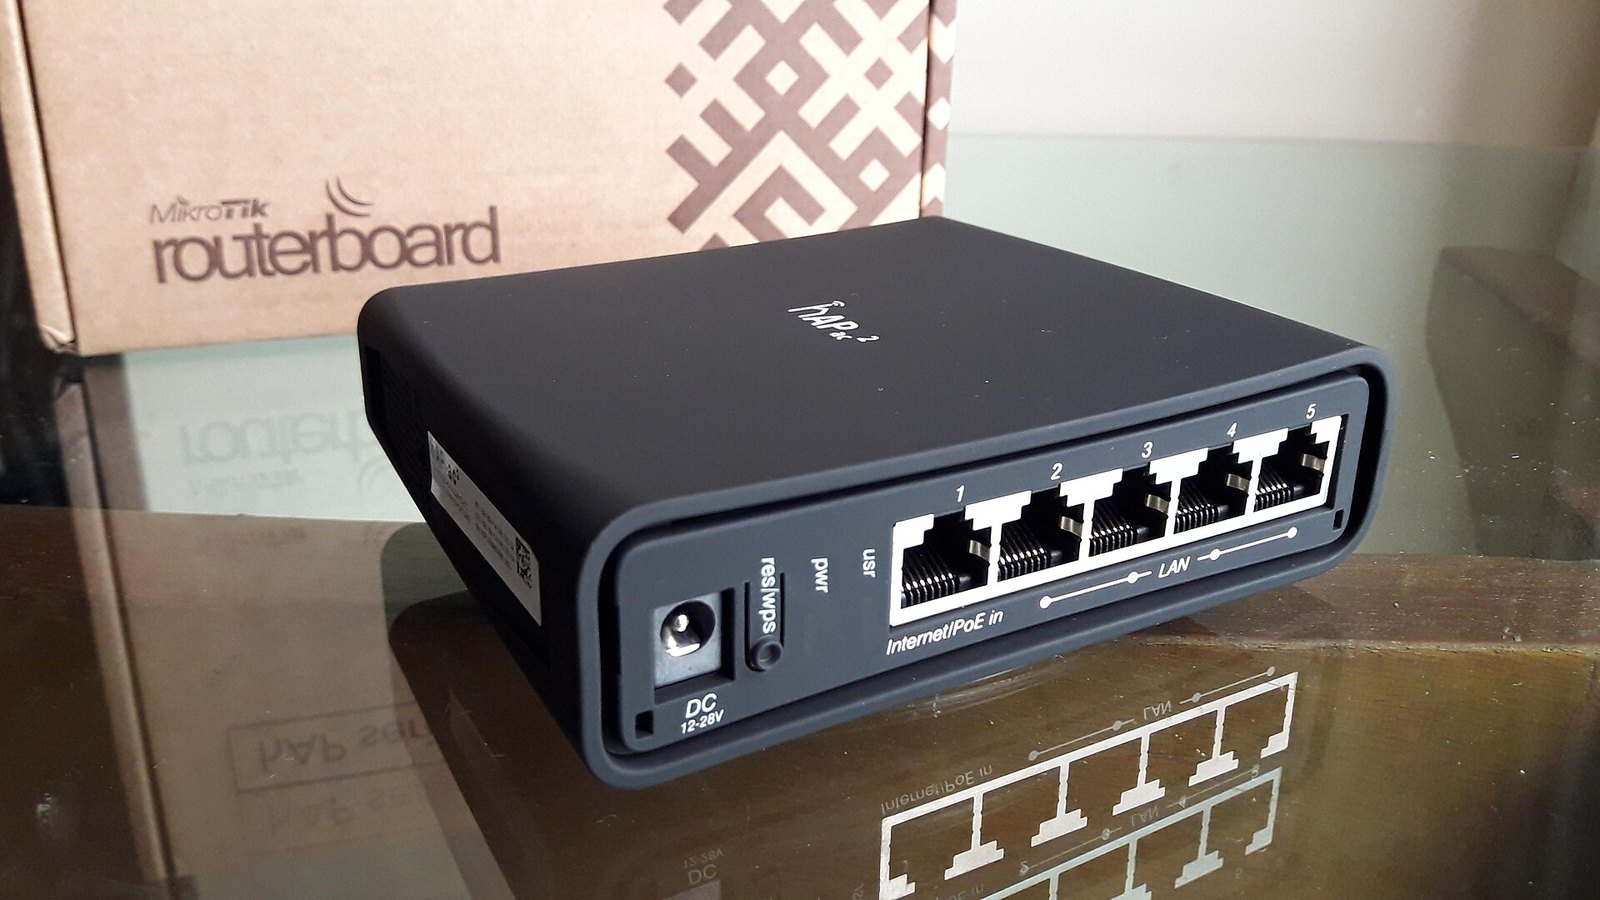
MikroTrick: when your edge router SSH port is the whole breach
CERT Polska named a two-CVE chain that gives unauthenticated admin control on internet-exposed MikroTik routers. Exploitation reportedly started before the public advisory. CISA added related RouterOS flaws to KEV with a September 13 federal deadline. Check SSH exposure and the flagged device marker today.
Mathew Potter
Security Analyst
GitLab's CVSS 10 flaw: one API call and your server files are readable
CVE-2026-85706 is a path traversal in GitLab's commits API. No login required. Honeypots saw exploitation within hours. CISA's federal deadline is September 14. If you self-host GitLab, read this before the weekend.
Mathew Potter
Security Analyst
Revolut handed over KYC files on a fake government email. No hack required.
A fintech confirmed it released passports, selfies, and Bitcoin transaction histories after fraudulent requests from a mailbox on a real government domain. Systems were not breached. Process was. That distinction matters for every regulated business.
Mathew Potter
Security Analyst
Berlin's 6TB leak: what Rhysida's government dump means for public sector security
Rhysida published roughly six terabytes of Berlin state government data after a refused ransom. Reporting ties the cache to administration and defense-related material. European public sector teams are watching closely. So should anyone with government clients.
Mathew Potter
Security Analyst
Cisco firewall managers under attack: what CVE-2026-20079 means for your network
Cisco confirmed active exploitation of a 10.0-rated authentication bypass in Secure Firewall Management Center. State actors and Qilin ransomware operators are in the mix. Federal agencies face a September 12 patch deadline. Here is what to check on your side.
Mathew Potter
Security Analyst
Stay updated
New briefing notes by email. No marketing list, and you can leave at any time.
We respect your privacy. Unsubscribe at any time.