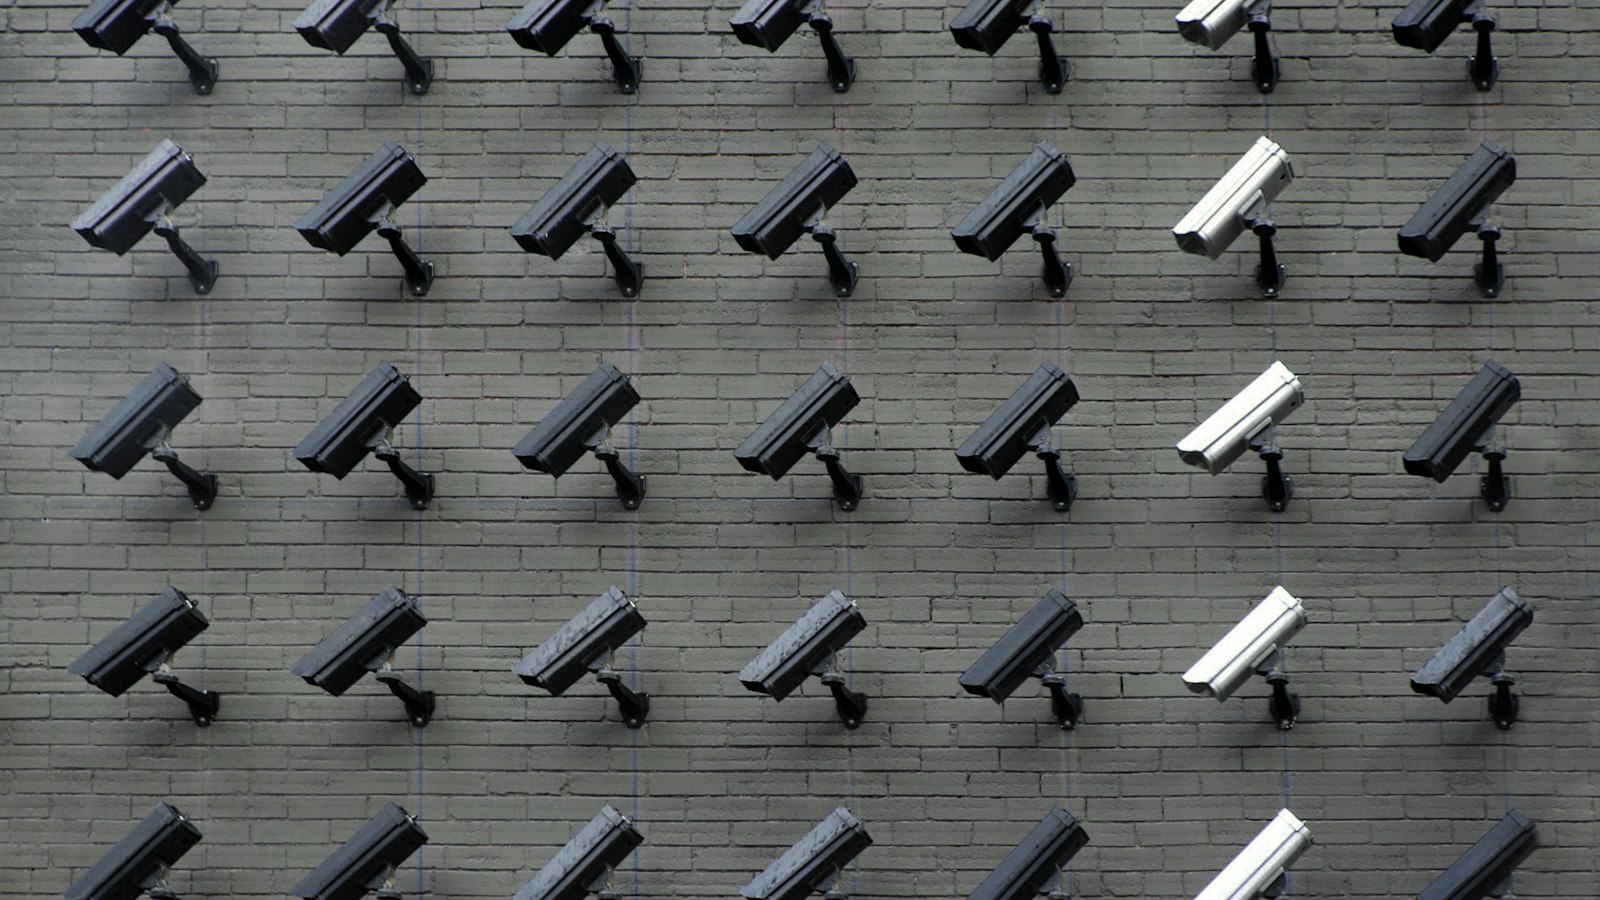
Someone pulled a Flock camera off a pole. The encryption key was on the camera.
WIRED and 404 Media analyzed a dumped Flock ALPR on September 16. On-device encryption kept its key on the device. About 1.6 million images over 21 days. The lesson for yards is older than Flock: lock the recorder and do not store the key next to the footage.
Today's security story is not another CVE spreadsheet. It is a camera that someone took off a pole.
WIRED and 404 Media published a joint investigation on September 16 into a Flock Safety automatic license-plate reader that a collective calling itself stegan0gram pulled from a roadway, imaged, and handed to journalists and to Distributed Denial of Secrets. Flock has sold these units as on-device encrypted. The recovered storage included an encryption key sitting on the camera itself. That key unlocked videos and stills. The recovered logs cover about 21 days of activity: roughly 50,200 vehicles and about 1.6 million images.
Taking someone else's camera and dumping it is illegal. We are not going to walk through how they did it. The useful part for anyone who actually runs cameras (yards, lots, shops) is what the dump proved about "encrypted at the edge."
The key lived on the box
Flock's public line, after a 2025 disclosure by researcher Jon Gaines, was that physical access still would not get you footage because images left the device quickly for the cloud. Today's reporting says otherwise. The hackers reached the Android system on the unit. Some partitions were unencrypted, including ones they described as vendor and media. The media partition held a key that opened another store of videos and stills.
That is an old lesson in a new wrapper. If the unlock material sits next to the ciphertext, you have delayed a thief, not stopped one. A lock on the pole and a lock on the recorder matter as much as the AES logo on the datasheet.
Flock's statement to WIRED was that unauthorized removal and tampering is illegal, that they run a vulnerability disclosure program, and that they did not get a report through that program with enough detail to assess the claims. Fair as far as it goes. It does not change what the journalists were able to open.
What the software actually saw
The camera runs a stack of Flock-built Android apps. Motion triggers a burst of stills (a typical vehicle produced about 28 images; some produced more than 100) plus short clips. Plate reading and make/model/color appear to happen on Flock's servers after upload, not on the pole. The on-device models do detect people, not only cars. WIRED ran those models over more than 27,000 recovered clips and found people in 11 of them, all motorcyclists, which matches a camera pointed down at a road. They found no evidence of face recognition beyond unused Android defaults. Flock says it does not do face recognition. That distinction still leaves a lot of identifiable imagery on a box you can unscrew.
The logs also show a device that was losing fights with its own disk: tens of thousands of "no space left" errors while trying to save full-resolution frames, plus crashes and reboots. An evidence system that fills up and overwrites is a finding even when nobody steals the hardware.
Same day, smaller cameras
OPSWAT's write-up of TP-Link Tapo C200 and C120 flaws is circulating again today. CVE-2026-15315 is an authentication bypass on the local network that can hand out an admin session without the owner's password (CVSS 8.7). CVE-2026-15316 can knock the management service over. TP-Link shipped firmware on August 18 (C200 v5 wants V5_1.4.6 or later). Same-LAN access is enough. That is the consumer version of the same problem: the camera is a computer, and "it is just a camera" is how it ends up on the office Wi-Fi next to payroll.
What this means if you run a yard, not a city
You probably do not run Flock. You run a handful of domes and an NVR in a closet, or a cloud kit the installer left on default ports. The Flock dump is still your problem set:
- Physical theft of a camera or a recorder is a cyber incident. Bolt the NVR. Do not leave the only copy of footage in a box a thief can carry.
- Do not store the backup of the encryption key on the same device that holds the video. If you cannot explain where the key lives, you do not have encryption. You have a delay.
- Retention you chose on purpose beats a disk that fills and starts throwing "no space" errors. Write the number of days down. Test an export before you need one.
- Keep cameras off the office LAN. A Tapo-class bypass on the same VLAN as file shares is a foothold, not a privacy oops.
- If the vendor's answer to a physical dump is "use our disclosure form," that is a process answer. Ask for a security answer: where is the key, what remains after a pull, and how long does identifiable footage sit on the pole.
We will not pretend ripping a public camera is research. We will say that "on-device encryption" that keeps the key on-device is a claim you should test before an insurer or a privacy commissioner asks.
Bottom line
Cyber and site security showed up as one story today. A camera is a computer on a stick. If someone can take the stick, assume they can take the week of video unless you designed otherwise. Forensic Five reviews camera fleets the same way we review servers: exposure, credentials, where the key lives, and whether an export would stand up. From St. Albert, Alberta. A site walk is not a requirement to buy hardware from us.
Tags
Table of Contents
About the Author
Mathew Potter
Security Analyst
Mathew leads assessments and consulting at Forensic Five from St. Albert, Alberta. His background is Linux systems, networks, and application infrastructure.